Client credentials grant flow
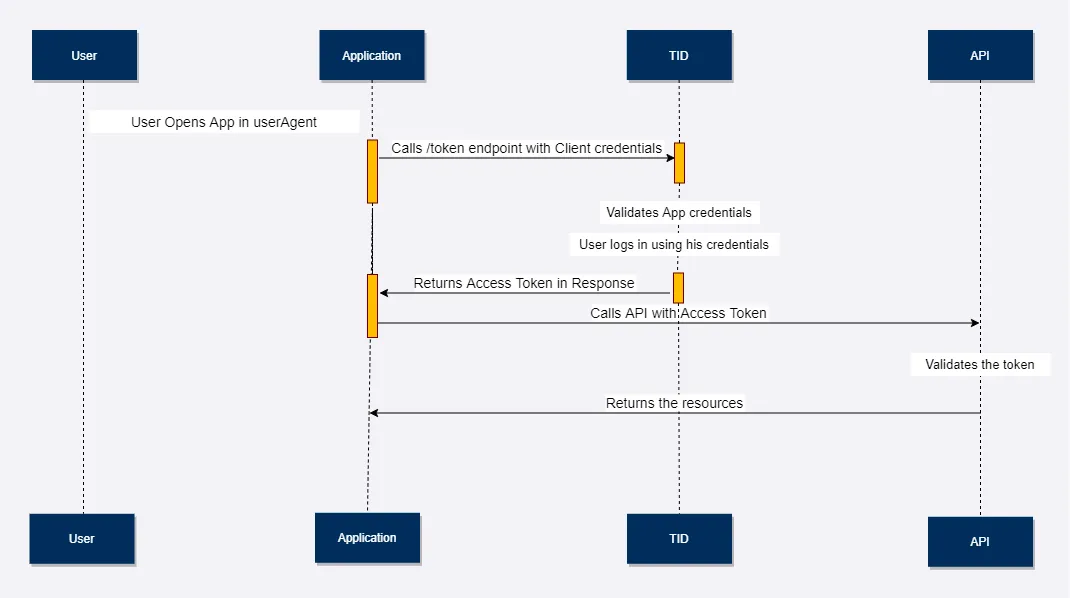
This method is used outside of the context of the user. The client is assumed to be the resource owner and the access request to an application’s resources rather than the resource’s owned by the user. An application access token should only be used in server to server calls and should not be used when making calls from a client-side application. The following diagram describes the Client Credential flow:
Token Request
Section titled “Token Request”-
API CALL:
- POST
{``baseURL``}/oauth/token
- POST
-
HEADER:
- Authorization: Basic <Base64 encoded “ClientID:ClientSecret”>
- Content-Type: application/x-www-form-urlencoded
-
BODY:
- grant_type = {client_credentials}
- scope = {ApplicationName} (Space separated values)
For scope, please do not use
scope=openidwith Client Credentials. The openid scope may be used with the Authorization Code flows in order to also return an id token.
Example request
Section titled “Example request”POST /oauth/token/Host: stage.id.trimblecloud.com/oauth/tokenAuthorization: BasicTE9pU...Content-Type: application/x-www-form-urlencodedAccept: application/jsonCache-Control: no-cache
grant_type=client_credentialsscope = processingToken response
Section titled “Token response”A sample response for the above request:
{ "access_token": "eyJ0e...", "token_type": "bearer", "expires_in": 3600}Account-associated applications in client credentials flow
Section titled “Account-associated applications in client credentials flow”When an application is associated with an account in Identity, access token generated for that application using the client_credentials grant includes the corresponding account_id claim in the access token JWT. The token request payload remains unchanged.
Decoded access token JWT (example with account association)
Section titled “Decoded access token JWT (example with account association)”{ "iss": "https://stage.id.trimblecloud.com", "exp": 1786103957, "nbf": 1786100357, "iat": 1786100357, "jti": "4c2a98b1cd1c46aca2c469828ebebfdf", "jwt_ver": 2, "sub": "5391c9cb-9c55-4544-a2c2-3f48d98076a3", "application_name": "regression_test_account_id_application", "identity_type": "application", "auth_time": 1786100357, "amr": [ "client_credentials" ], "account_id": "regression_test_account_id", "aud": [ "5391c9cb-9c55-4544-a2c2-3f48d98076a3" ], "scope": "regression_test_account_id_application", "sub_trn": "trn:2:iam:us:application:5391c9cb-9c55-4544-a2c2-3f48d98076a3"}- To decode and verify the TID JWT Token, refer to Decode JWT